Of the many useful things I could do with my spare time instead I’m setting up a Lemmy instance because why not. The scope of this is definitely greater than any self-hosting I’ve ever attempted, so please feel free to tell me just how much trouble I’m in. I’m just giving the broad strokes to see if I’ve made any crucial errors (other than deciding to do this at all).
And if this is a completely wrong place for a post like this or I’m missing data I’m supposed to include I apologize, I probably need a sanity check, in more ways than one.
First limitation, I’ll be hosting it on an existing Linux Mint box acting as a file share mostly and occasional gaming PC/movie streaming box. Its hardware is overkill for this, I do not anticipate issues when it is in use. It receives regular updates and weekly reboots, instance will be set to automatically restart. NVMe with loads of space for local storage, RAID SSDs for data offload/backup.
Second limitation, I hate Cloudfare and Oracle. I do not want to use either of them.
Third limitation, money. Cheaper is better. I have a URL picked out and a registrar which will give me the cheapest long term option, in case I actually keep this thing going.
Last limitation, I’m already in over my head so I’ll be relying on a lot of googling and probably some chat bots to figure things out as I go through the actual deployment process. What could go wrong?
So, Lemmy hosted on Linux Mint box using Docker containers. ISP is a good one for this I’m told, no CGNAT, largely stable public IP but I’ll have a script running in case it does change. Confirmed ports 80/443 are open. Using Caddy for the HTTPS. Closed registration to start, if by some miracle I make it to actually wanting to allow additional users it will not be fully open, and I’ll use Brevo for the email SMTP. Security wise I know I’m making it harder for myself by exposing my IP, I’m going to have UFW running and Crowdsec to help keep incoming bad traffic out.
Down the line I’ll get Lemmy updates, backups, retention rules in place/automated, and make decisions on federation, etc. Thoughts?
Yes. Do PieFed.
Also, don’t do cloudflare. If you must use something, make sure it’s self hosted.
Do it. You’ll learn something new. Maybe you’ll even contribute to the code.
Best of luck to you!!! I just went through this last week and wow it was a challenge. I went the docker route not using ansible…and yah by far the worst install I ever went through of all the self-hosting projects I have setup…but my setup was largely complicated by the fact I had an Apache reverse proxy setup in front of the nginx proxy that has an example config provided…finally figured it all out, but yah fun times 😂 happy to help if you get stuck.
One of my earlier deployment plans had me using Ansible, then a bot aided revision had me remove it since I’m doing a single machine install and a fairly straightforward process. From my understanding I’ll get a better learning experience not using it so I figured that was better.
Yah i had never used it either, alot of the tutorials I found suggested it, and what threw me for a loop and was the ultimate Aha! moment for me was there is an ansible version and a non ansible version for the docker configs with different options in each, and the ultimate key thing I overlooked is on github, I kept using the “main” development branch which had changes that didn’t work with the stable .19 version. Switching to the .19 branch on GitHub and referencing those configs made it all click
Not sure what your solution was, but I eliminated the reverse proxy from the official compose stack and configured my existing reverse proxy to point directly at the lemmy containers. It works well for me.
Thanks. Yah that was what I tried to accomplish using Apache but couldn’t get the correct proxypass statements in Apache that would do the correct passing depending on the header received. Tried asking an LLM for help but never got it to work, so ended up doing a basic/straight pass through apache to a local VM running nginx as an outer proxy which proxy’s to the nginx internal proxy…its messy as all hell but it works 🤷
I don’t know enough about Apache to say one way or the other, but based on what you described, you SHOULD be able to get rid of the internal proxy. Since both the inner and outer are both NGINX, getting the settings right shouldn’t be a problem.
But, on the other hand, if it works it works!
Good call. Perhaps on a rainy day I’ll take another crack at it…but yah the ports are exposed through docker so yah, makes sense. Thanks and have a great day!
I would not do that without first looking into applicable laws regarding legal liability for content and requirements to remove things. Depending on where in the world you are, this can be a minefield.
Especially because Lemmy devs don’t five a fuck about instance admins liabilities or gdpr
Not necessarily, but why choose a project that needs interfacing with an existing ecosystem where it can mostly only be noise?
If you want to deal with a complicated mess of a system as a project, you could always grab Arch
Acronyms, initialisms, abbreviations, contractions, and other phrases which expand to something larger, that I’ve seen in this thread:
Fewer Letters More Letters DNS Domain Name Service/System ISP Internet Service Provider NAT Network Address Translation TLS Transport Layer Security, supersedes SSL VPS Virtual Private Server (opposed to shared hosting) nginx Popular HTTP server
[Thread #76 for this comm, first seen 11th Aug 2026, 19:20] [FAQ] [Full list] [Contact] [Source code]
We need more of this across all Platoforms for discovery and learning. Thank you!
How much RAM do you have available? Do you have an unlimited internet connection?
32gb, not unlimited but good enough that I am willing to proceed, then limit bandwidth usage through restrictive federation.
Great, that should be plenty! Smart to restrict, federation indeed results in a ton of traffic :D
Thought about doing something very similar, I’ll be curious to hear the feedback and your experience
If at some point in the near future you step outside and hear a weird screaming sound echoing around the globe, that’s me.
I did a very similar setup very recently. Its not bad. I did try piefed first as some people suggested, but had some issues and it felt like it just wasn’t ready yet. I switched to self hosting lemmy and really like it. I also went with Brevo for email (I started with sendgrid, would not recommend).
Main difference for me is I am using cloudflare (they are my registrar and they allow me to deal with the CGNAT at no extra cost which you don’t have to deal with not to mention a pretty solid WAF for free tier). You may want to implement a WAF of some kind to keep the federation in check. I federate both lemmy and a matrix home server and it doesn’t eat up too much bandwidth.
I also like saving money, so a VPS is something I was trying to avoid. Personally, I don’t think the VPS does a much for securing your home network as people are trying to say here. It is another layer of security, but it’s not a panacea. Not saying I’ll never try it though.
I actually started on a VPS… I moved off because I was pegging the RAM and adding more to my plan was quite expensive. Performance is MUCH better on my home server with plenty of RAM.
The problem is not the setup but the administration
So I’m discovering, heh. I got the instance up in a relatively short period of time, I’m spending far more time on email, domain, logging, backups, decisions, etc. I know I could just be a barebones “who cares about any of that” instance since it’s largely gonna be my own personal playground, but where’s the fun of that?
Yes, you are, but aren’t we all?
Lemmy eventually plans on having an invite system, you could maybe use that when it comes out
https://github.com/LemmyNet/lemmy-ui/issues/4128
(You can also do this manually with the application questionnaire field and a spreadsheet)
I probably wouldn’t host it at home, there are so many personal devices containing personal information on the network that I don’t consider the risks involved worth it. I would get a VPS, even if they’ve increased in price lately. If you do set it up at home, you will have to harden the server and the network, and that requires a lot of time, knowledge and effort. Just keep this in mind!
You can easily sequester your personal stuff from your self hosted stuff. Most traffic going anywhere is encrypted as it should be. The main concern is lateral movement hence the network isolation.
Yes you are mad, I know as I did that over 3 years ago. Went from at home => a cheep VPS => paid for Oracle VPS.
If you go down the lemmy route (vs piefed) then I would deply with Lemmy-Easy-Deploy by @ubergeek77. this makes setting Caddy and mail simple
Good to know, I’ll take a look at those. Thanks!
up untill now I’ve not had too much bot traffic, but I’m betting hammered atm. Make sure to have some good firewall rules for when it happens:

check this out!
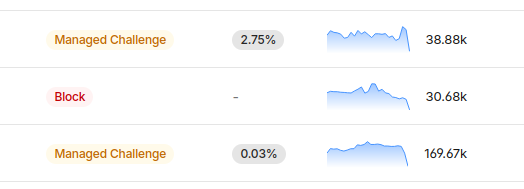
those ~2000 blocks were in the hour after turning on the full proxy, still getting a fair few from china hitting the real IP address that they must have cached.
Grep’d the logs and had 250,000 requests from china in the last 20 hours asking for full threads via the api
Update with a link to your instance when you’ve done it so we can show some love and support